Hacking News Breaking Cybersecurity. No Filter.

Hacking News

Breaking Cybersecurity. No Filter.

Latest Articles

When the Assembly Line Gets Hacked: Why Your Build Server Is the Most Dangerous Machine in Your Stack
Investigation

When the Assembly Line Gets Hacked: Why Your Build Server Is the Most Dangerous Machine in Your Stack

Attackers aren't bothering to crack your code anymore — they're going after the machines that compile it. A wave of sophisticated intrusions targeting CI/CD build infrastructure is quietly turning trusted software pipelines into delivery vehicles for enterprise-grade malware, and most security teams aren't even looking in the right direction.
Phantom Patches and Ghost CVEs: How AI Hallucinations Are Being Turned Into Cyber Weapons
Investigation

Phantom Patches and Ghost CVEs: How AI Hallucinations Are Being Turned Into Cyber Weapons

Security teams are getting played by convincing-but-fake threat intelligence generated by AI models that simply made things up. From fabricated CVEs to ghost advisories, attackers are learning to weaponize the one thing defenders trust most — their own tools.

Always Listening, Always Selling: The Hidden Data Economy Living Inside Your Smart Speaker
Investigation

Always Listening, Always Selling: The Hidden Data Economy Living Inside Your Smart Speaker

Your Amazon Echo and Google Nest aren't just waiting for wake words — they're part of a sprawling data pipeline that funnels behavioral audio signals to brokers you've never heard of. We dug into the technical reality of what these devices actually capture, which companies have the worst records, and the legal loopholes that make all of it completely above board.

The Blinking Light on Your Desk Is Watching You: How Office Printers Became the Perfect Hacker Entry Point
Investigation

The Blinking Light on Your Desk Is Watching You: How Office Printers Became the Perfect Hacker Entry Point

Security teams spend millions locking down endpoints, firewalls, and cloud infrastructure — then leave the $400 multifunction printer in the corner completely unpatched for three years. Attackers have noticed. Here's how they're walking through that open door and what your team can do before the next breach audit finds it first.

Your Face Is No Longer Your Password: The Rise of AI-Cloned Identities Cracking Biometric Gates
Investigation

Your Face Is No Longer Your Password: The Rise of AI-Cloned Identities Cracking Biometric Gates

Attackers are no longer just guessing passwords — they're synthetically rebuilding your face. A new wave of AI-generated video attacks is quietly dismantling the biometric authentication systems that enterprises and consumers were told were unbreakable. Here's what's actually happening on the front lines.

Turned Against the Team: How Attackers Are Quietly Converting Your Security Staff Into Their Best Asset
Investigation

Turned Against the Team: How Attackers Are Quietly Converting Your Security Staff Into Their Best Asset

The people you've hired to protect your organization may already be compromised — not through malware, but through manipulation. A growing body of evidence shows threat actors are deliberately studying security team dynamics, access privileges, and internal culture to flip defenders into unwitting accomplices. Here's how it happens, and why most companies never see it coming.

Ghost Sessions: How Hackers Are Raiding Your Browser's Memory Without Touching Your Password
Investigation

Ghost Sessions: How Hackers Are Raiding Your Browser's Memory Without Touching Your Password

You changed your password. You enabled MFA. You did everything right — and they still got in. The dirty secret of modern authentication is that your password is often the least interesting thing an attacker wants. What they're really after is already sitting in your browser's memory, waiting to be scooped up.

Hunting the Hunters: The Calculated Playbook Threat Actors Use to Flip Security Pros Into Victims
Opinion

Hunting the Hunters: The Calculated Playbook Threat Actors Use to Flip Security Pros Into Victims

Security engineers spend their careers learning to spot manipulation — and attackers know it. The most dangerous social engineering campaigns aren't aimed at the receptionist or the new hire anymore. They're precision-crafted for the people who are supposed to stop them, and they're working.

They Read Your Slack Before They Phished You: How Attackers Are Mastering Your Company's Culture to Walk Right Through the Front Door
Opinion

They Read Your Slack Before They Phished You: How Attackers Are Mastering Your Company's Culture to Walk Right Through the Front Door

Modern social engineering attacks aren't just spoofing email addresses anymore — they're spoofing entire corporate identities. Threat actors are spending weeks studying org charts, internal lingo, office politics, and team dynamics before making a single move. The result is attacks so culturally fluent that even security-aware employees get fooled, and the playbook is getting more sophisticated by the month.

Trojan Weights: The Hidden Threat Lurking Inside Every Pre-Trained Model You Pull from the Internet
Investigation

Trojan Weights: The Hidden Threat Lurking Inside Every Pre-Trained Model You Pull from the Internet

Researchers are sounding the alarm on a new class of supply chain attack that doesn't target your code — it targets the AI models you're plugging directly into production. Poisoned neural networks are quietly making their way through Hugging Face, GitHub, and other popular repositories, carrying malicious behaviors that no antivirus on earth will catch. Here's what's actually happening, and why the security community is only beginning to understand the scope.

Passwordless Was Supposed to Save Us. So Why Are We Still Typing 'Password123'?
Opinion

Passwordless Was Supposed to Save Us. So Why Are We Still Typing 'Password123'?

The security industry declared passwords dead years ago. FIDO2, WebAuthn, and passkeys were supposed to bury them for good. But walk into almost any American enterprise in 2024 and you'll find the same sticky notes on monitors, the same quarterly password resets, and the same help desk tickets about forgotten credentials. Here's why the post-password future is taking forever to arrive.

The Phishing Email That Knows Your Boss's Writing Style — AI Did That
Investigation

The Phishing Email That Knows Your Boss's Writing Style — AI Did That

Generative AI didn't just make phishing emails better-written — it made them personal, scalable, and nearly impossible to catch with traditional filters. Security researchers are documenting a new generation of AI-assisted social engineering attacks that can clone communication styles, adapt in real time, and defeat the defenses most organizations have spent years building. This is what that looks like from the inside.

Selling Holes in the Internet: The Shadowy Marketplace Where Zero-Days Go to the Highest Bidder
Investigation

Selling Holes in the Internet: The Shadowy Marketplace Where Zero-Days Go to the Highest Bidder

There's a thriving underground economy where a single undisclosed software flaw can fetch more than a luxury car — or a house. We dug into the murky world of zero-day trading to find out who's buying, who's selling, and what it means for every enterprise security team trying to keep the lights on.

Your Inbox Is Being Targeted by a Machine That Knows You Better Than Your Coworkers Do
Opinion

Your Inbox Is Being Targeted by a Machine That Knows You Better Than Your Coworkers Do

Generative AI didn't just make phishing emails better — it made them terrifyingly personal. The old tells are gone, and the attacks are scaling in ways that traditional email security simply wasn't built for. Here's what's actually happening out there, and what you can realistically do about it.

Poison in the Pipeline: How Compromised Open-Source Packages Are Quietly Owning Your Codebase
Investigation

Poison in the Pipeline: How Compromised Open-Source Packages Are Quietly Owning Your Codebase

Attackers have figured out that they don't need to break down your front door if they can slip something nasty into the lumber you're using to build it. Supply chain attacks targeting npm, PyPI, and other package ecosystems are skyrocketing — and most dev teams are flying blind.

The Master Key Problem: Password Managers Promise Safety — But What Happens When They Get Hacked?
Opinion

The Master Key Problem: Password Managers Promise Safety — But What Happens When They Get Hacked?

Password managers are supposed to be the gold standard of personal security hygiene. But a string of high-profile breaches has security professionals asking an uncomfortable question: is storing every credential you own in one place actually brilliant — or is it the biggest single point of failure you've ever created?

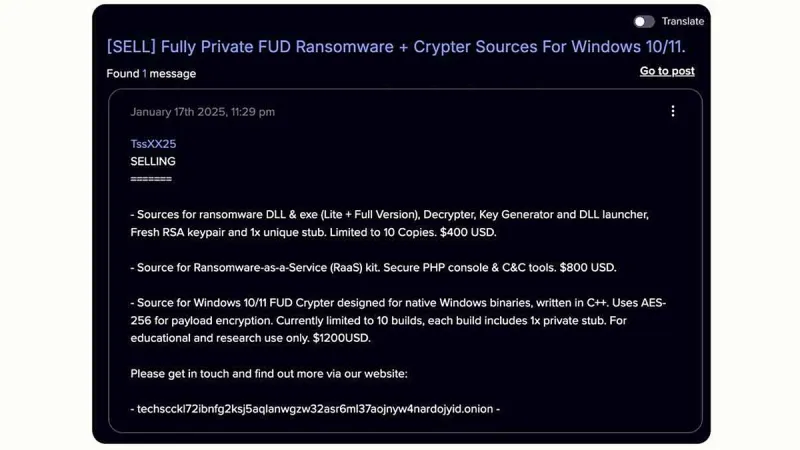
Ransomware Went Corporate: Inside the Underground Franchise Model Bleeding US Businesses Dry
Opinion

Ransomware Went Corporate: Inside the Underground Franchise Model Bleeding US Businesses Dry

Ransomware isn't a hacker in a hoodie anymore — it's a full-blown criminal enterprise with affiliate programs, SLAs, and customer support portals. We break down how the Ransomware-as-a-Service economy became a $50 million juggernaut, why US companies keep getting hit hardest, and what the latest law enforcement crackdowns actually accomplish.

Your Code Is Leaking: The Silent API Key Crisis Hiding in Plain Sight on GitHub
Investigation

Your Code Is Leaking: The Silent API Key Crisis Hiding in Plain Sight on GitHub

Thousands of companies are unknowingly handing attackers the keys to their kingdom — and those keys are sitting right there in public GitHub repos. We dug into the scale of the problem, how automated scanners are exploiting it around the clock, and what your security team needs to do before someone else finds your secrets first.